Same Attacker, Another Clinic. The Medyc Data Breach Exposes Weeks of Silence on Poland's GDPR Breach-Notification Duty
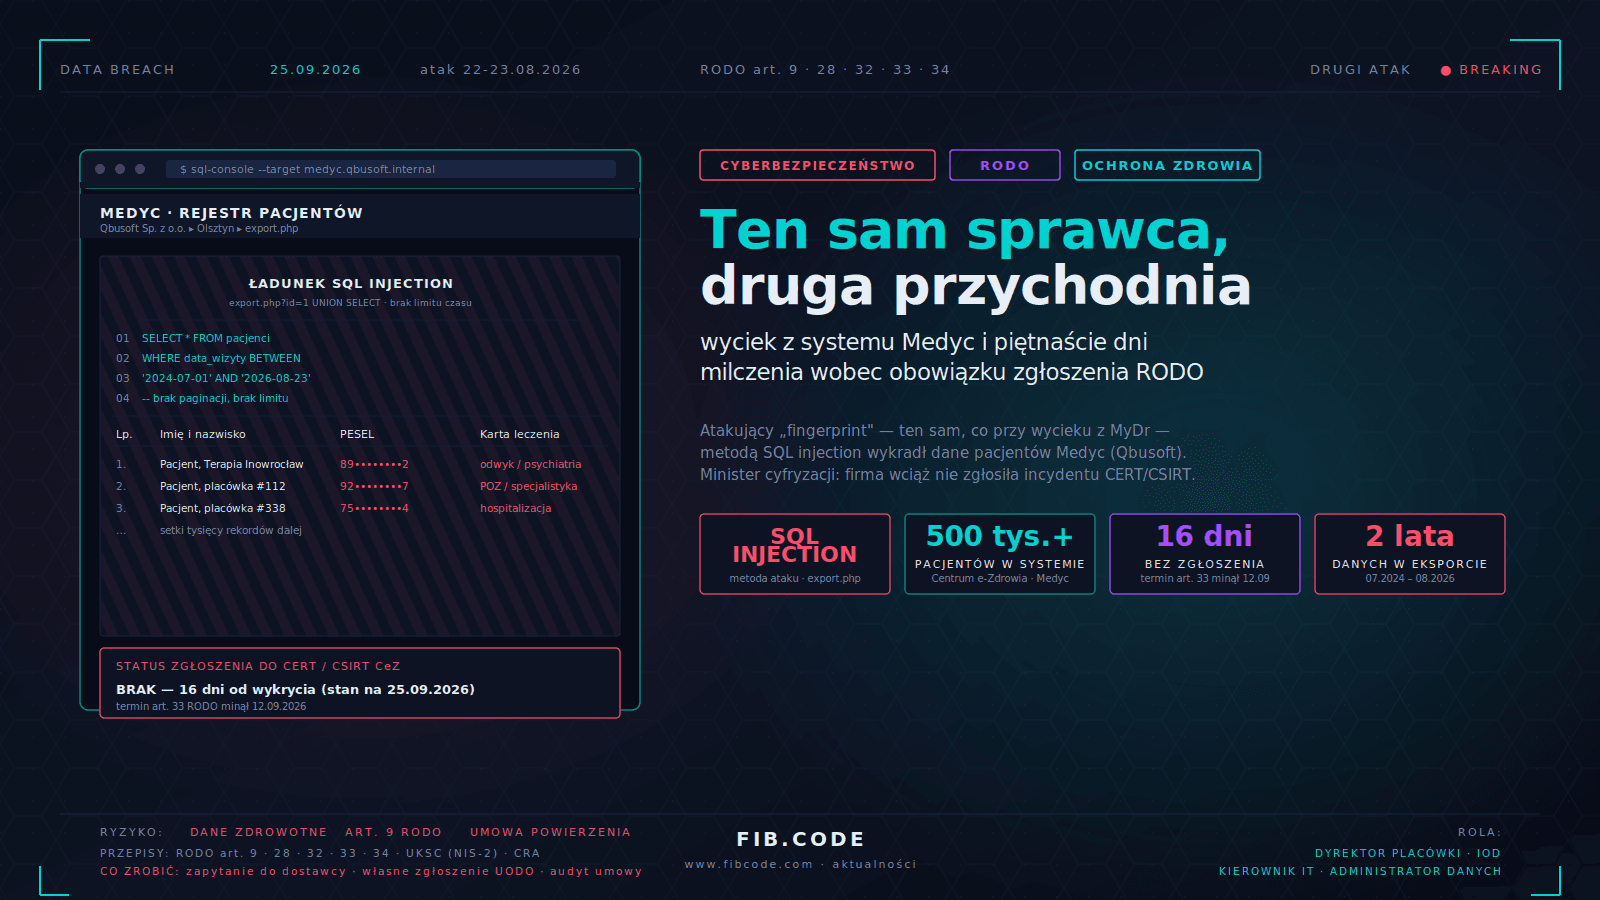
On 22 August 2026 the same attacker behind the earlier MyDr leak used a SQL injection flaw to break into Medyc, the patient-registration software built by Olsztyn-based Qbusoft and used across hundreds of Polish medical facilities. Names, PESEL numbers, addresses and hospital discharge records leaked, including files from an addiction and psychiatric treatment centre in Inowrocław. Qbusoft learned of the breach on 9 September, yet — as Digitalisation Minister Krzysztof Gawkowski confirmed on 25 September — has still not reported it to CERT Polska or CSIRT CeZ, sixteen days after discovery and thirteen days past the statutory GDPR Article 33 deadline. We explain who in the vendor-controller chain carries the liability, what a correct breach notification looks like, and why every facility running third-party medical software should check its data processing agreement today.
GDPRUODOCybersecurity+5